This week was our usual set of monthly SDK releases. We also released improvements to our weekly security briefing emails, added Nonce access to the Nosecone API, and opened the first version of our new activity view in the Arcjet Console.
JS, Python, Go SDK releases
We aim for monthly SDK releases to minimize version churn whilst adding new functionality.
- The JS SDK 1.6 includes proxy support and the new optimized Wasm bundle I wrote about a few weeks ago.
- The Go SDK had it's first numbered release - 0.1.0 - and includes improved per-request caching and the new Wasm bundle as well.
- The Python SDK was also updated to include the new Wasm bundle.
Weekly security briefing improvements
Every Monday we email a security briefing to all users. This now includes more detailed threat tagging, country-breakdowns, and updated recommendations when we see suspicious traffic.
Nosecone Nonce API
Arcjet Nosecone is an open source library that helps set security headers such as Content-Security-Policy (CSP), Strict-Transport-Security (HSTS), and X-Content-Type-Options in JS applications built with Bun, Deno, Next.js, Node.js, or SvelteKit.
We latest 1.6.1 release includes an API so you can access the Nonce in Next.js. This is usually applied to scripts automatically if you use the <Script> component, but that is not universally supported. Use new the nonce function to read the nonce for the current request from a Server Component, Route Handler, or anywhere else next/headers is available:
import { nonce } from "@nosecone/next";
export default async function Page() { const cspNonce = await nonce();
return <script nonce={cspNonce}>{`/* ... */`}</script>;}Console activity view
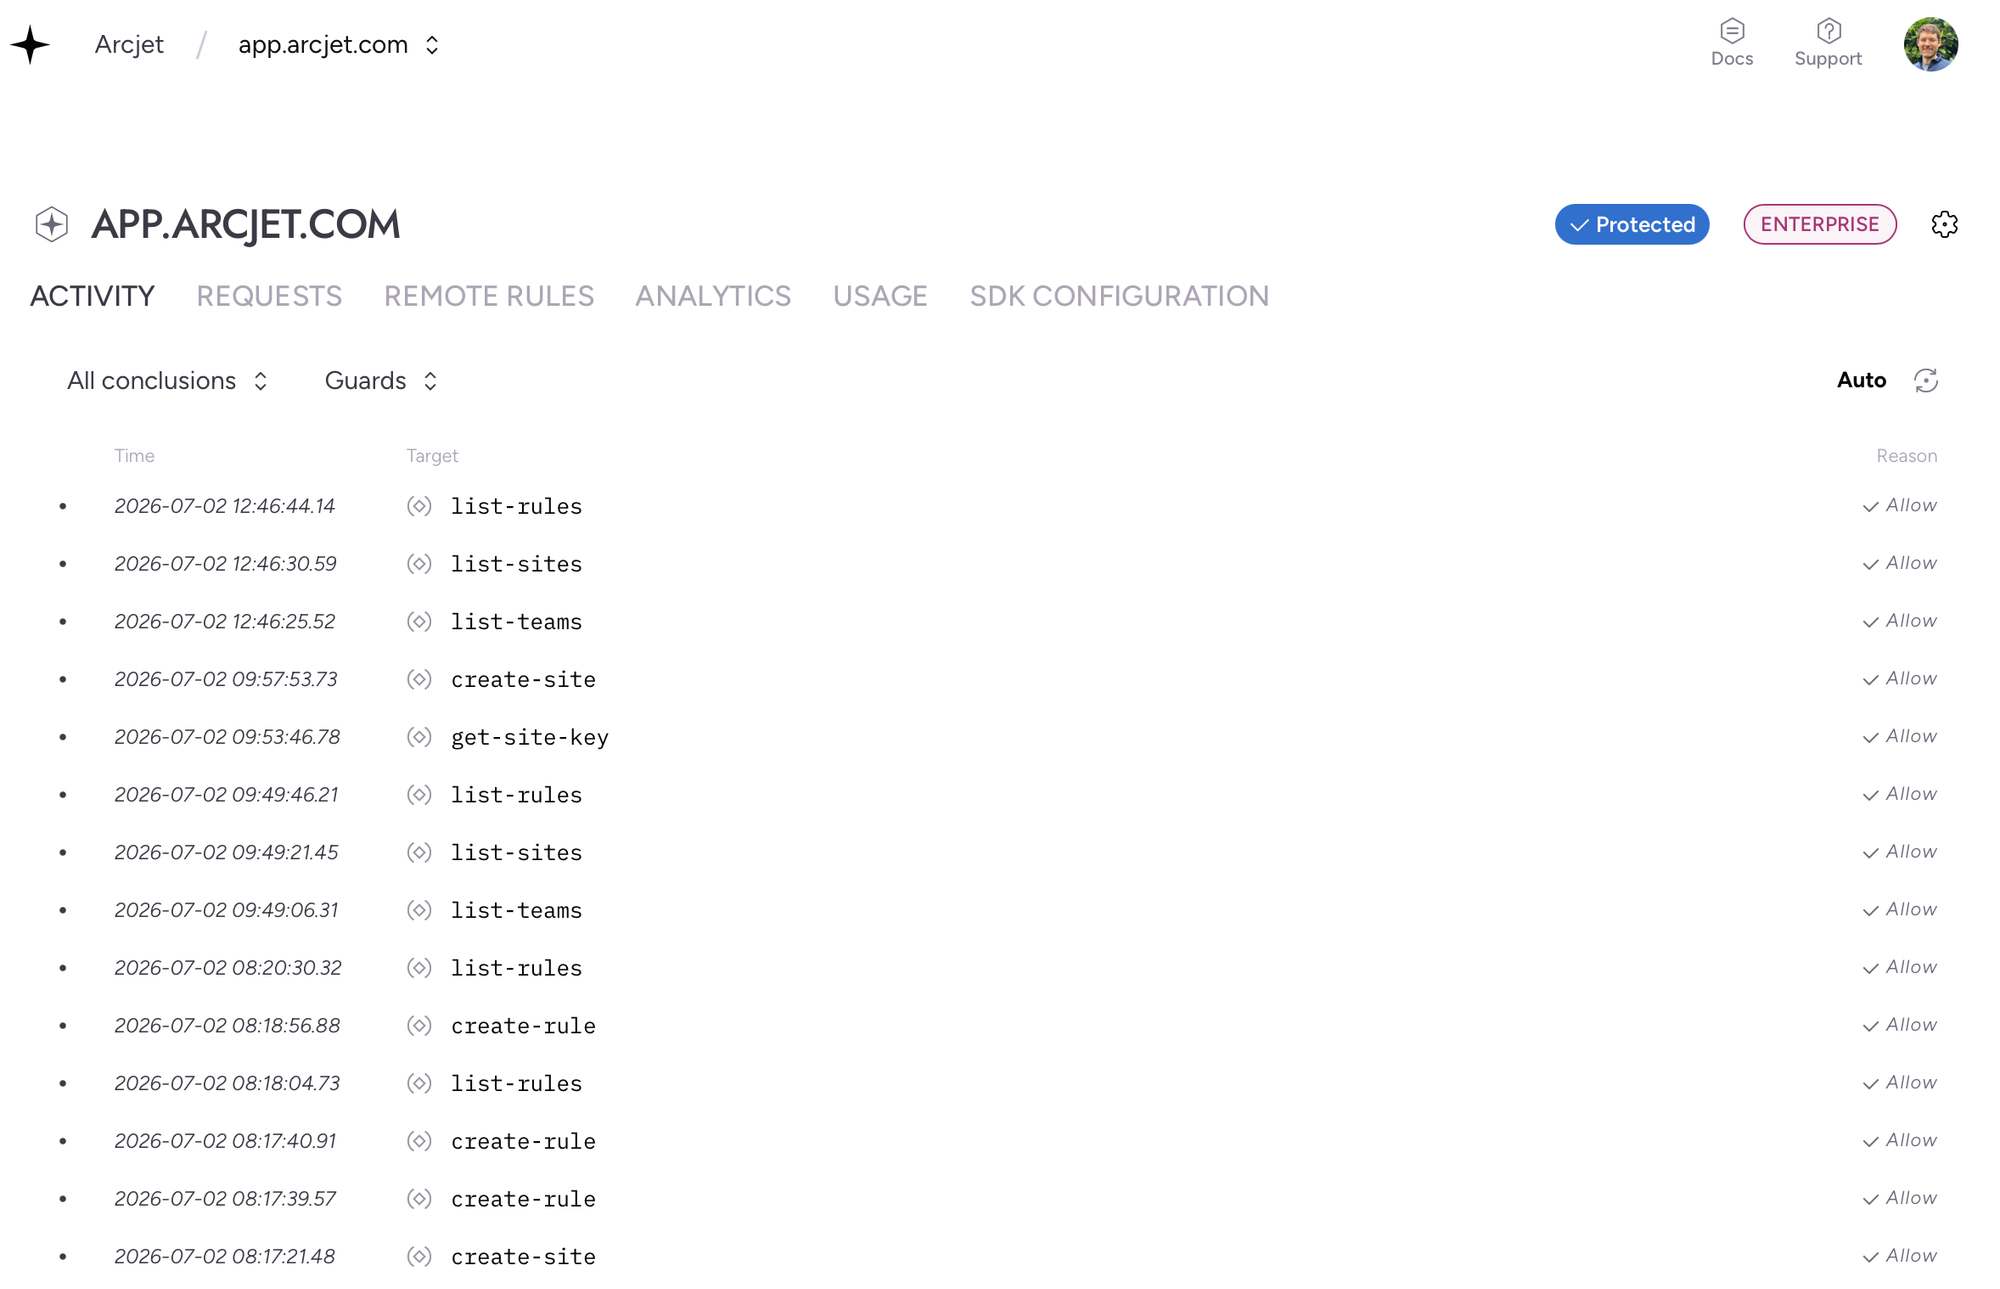
Arcjet Guards operate on events triggered without an HTTP context, often following a web request e.g. a chat UI triggering a file access in an agentic application. These are now visible in the Arcjet Console on a new activity view alongside web requests. Over time we'll be merging these two views.
🚀
Try Arcjet
Security that ships with your code
Protect AI agents and applications with rules that run where your code runs — rate limiting, bot detection, shield, and Guards.